Skip to content
IDENTITY VERIFICATION · PRODUCT SERIES

M802Smart Face Verification Terminal

A dedicated identity-verification station designed for clear on-site interaction. Deploy the M802 on its own, or pair it with the H601 RFID access lane for a project-specific access configuration.

✓ Standalone deployment✓ Optional H601 integration✓ Dual-screen display
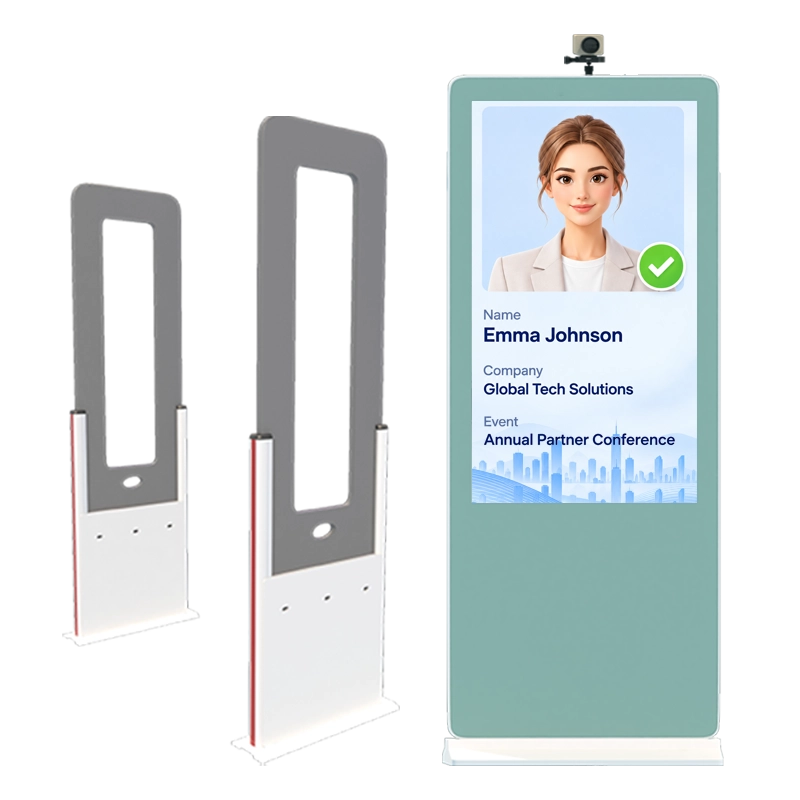
M802 face verification terminal with H601 RFID access lane
43-inch + 23.6-inchMain and secondary displays
≤ 1 secondPublished access response time*
ISO 15693Long-range RFID card protocol support
Optional H601Accessible RFID lane configuration
One terminal · Two deployment options

Start with one device.
Scale to a connected lane.

Choose the configuration that fits your site, visitor journey and access-control requirements. System behaviour depends on the selected software, interfaces and project integration.

Option 01 / Standalone

M802

A self-contained verification station for projects that need an on-site identity-checking point without adding a physical lane.

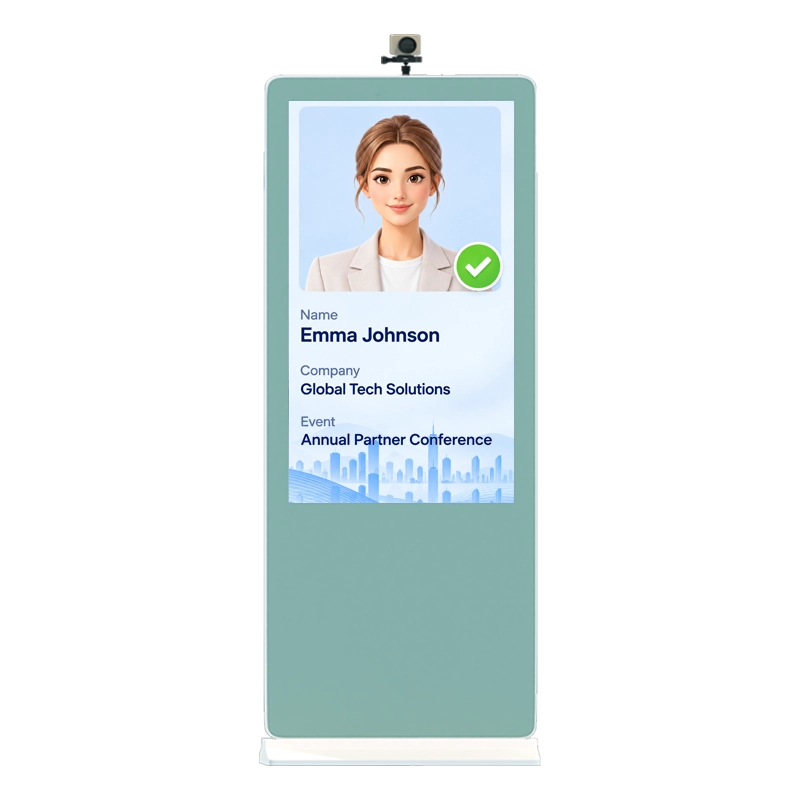
M802 terminal product view
  • Dual-screen interaction and information display
  • On-site face capture and identity comparison workflow
  • Can be deployed as an independent terminal
  • Suitable for reception, check-in and verification points
A practical starting point for identity-verification workflows.
Designed for on-site workflows

Verification made visible.

Bring identity checking and operator feedback into one clearly presented station.

Dual-screen display

A 43-inch main display and 23.6-inch secondary display support a more visible on-site interaction.

Face capture & comparison

Supports dynamic face detection, tracking, image analysis, capture and identity comparison workflows.

RFID support

Supports the ISO 15693 protocol for long-range RFID card applications, subject to the configured system.

Configurable verification

Whitelist verification and blacklist alerts are described in the product information; implementation depends on the deployed software and policy.

Audio prompts

Voice prompts can provide feedback during the verification process.

Optional lane linkage

Can be specified with the H601 lane where the project requires an integrated access workflow.

A configurable workflow

From identity check
to the next step.

A simple way to explain the system at a project level. The exact sequence and access decision are defined by the customer’s configured system and operating policy.

01 / PRESENT

Person arrives

The visitor or credential holder approaches the designated verification point.

02 / VERIFY

M802 checks identity

The terminal performs the configured face-capture and identity-comparison workflow.

03 / PROCEED

Configured next action

Display a result or, in an integrated project, coordinate with the access-control lane as configured.

Application environments

Built around real entry points.

Adapt the deployment to the operational context, the people using the site and the applicable local requirements.

01 / EVENTS

Conferences & exhibitions

Attendee check-in and identity-verification points.

02 / ENTERPRISE

Corporate sites

Employee and visitor verification workflows.

03 / EDUCATION

Campus environments

Configured identity checks for campus entry and events.

04 / VENUES

Public venues

Project-specific verification and passage management.

Product information

Technical overview.

Key specifications published for the M802 model. Confirm the latest configuration and regional electrical requirements with the sales team before ordering.

Request full datasheet ↗
ModelM802 Smart Face Verification Terminal
Overall dimensions635 × 440 × 1,560 mm
Main display43-inch LCD
Secondary display23.6-inch LCD
Main control moduleIntel Core i7-6700K (published configuration)
Memory / Storage4 GB RAM / 128 GB SSD (published configuration)
InterfacesMore than 6 USB ports; 1 COM port
Power supplyAC 220 V (+10% / −15%)
Access response time≤ 1 second (published figure; test conditions should be confirmed)
RFID protocolISO 15693
Optional laneH601 accessible RFID lane

Specifications are reproduced from currently available product information and may vary by production batch, software version or project configuration. Please request a current datasheet for confirmation.

Responsible deployment

Privacy and compliance
are part of the project.

Biometric verification requires careful planning. The device itself does not make a deployment automatically compliant with privacy or data-protection laws.

Plan the complete data lifecycle

Before using face recognition, the deploying organisation should assess the applicable laws and document how personal and biometric data will be handled.

  • Identify and document an appropriate lawful basis and, where required, an applicable condition for processing biometric data.
  • Provide clear notices explaining the purpose, controller, retention period, recipients and individual rights.
  • Collect only the data needed, restrict access, protect stored data and define deletion procedures.
  • Assess whether a Data Protection Impact Assessment or other local assessment is required before deployment.
  • Provide an appropriate alternative route where required by law or by the organisation’s policy.

For EU/UK deployments, biometric data used for uniquely identifying a person can be subject to special-category rules under data-protection law. US requirements vary by state and use case, including specific biometric privacy laws. Obtain advice from qualified privacy counsel for the intended deployment. This page is product information, not legal advice.
Discuss your project

Looking for the right verification setup?

Tell us about your site, workflow and integration requirements. We can help you review the M802 standalone and M802 + H601 configurations.

Contact Us ↗